




Google is presenting Google Multi-Party Compute, a crypto custody service for financial institutions, at its inaugural digital assets symposium in New York on 28th October, 2026. The company says it has never offered a dedicated multi-party computation (MPC) custody product for cryptocurrencies before.
Key Facts
- Google Multi-Party Compute is in private preview, with design partners and major financial institutions testing it ahead of a commercial launch.
- Alphabet, Google’s parent company, already uses the system to secure its own digital assets on Ethereum and Solana.
- Fireblocks, Fordefi and BitGo, which sell transaction security tools to institutions, now face competition from one of the world’s largest cloud providers.
- Private-key compromises account for roughly 40% of the cumulative $16.69 billion blockchain projects lost to hacks and exploits through June, DeFiLlama data shows.
Google bundles MPC signing into one service
Google has worked with MPC before. In 2023, it published guidance showing customers how to build MPC-based digital asset systems on its Confidential Space infrastructure. Institutions also rely on its Cloud Key Management Service (KMS) and Cloud HSM to manage and protect cryptographic keys.
What changes is the packaging. The new product folds MPC-based signing, transaction policies and key recovery into one service, so customers no longer assemble those pieces themselves.
Banks are exploring blockchains to issue tokenized assets, process payments and offer custody, and completed on-chain transfers generally cannot be reversed. Rich Widmann, director of digital assets strategy at Google Cloud, told CoinDesk that regulated institutions “need scalable, proven infrastructure to secure their clients’ assets.“
JUST IN: Google is building security systems to help banks store and transfer crypto
— Kalshi Crypto (@Kalshi_Crypto) October 28, 2026
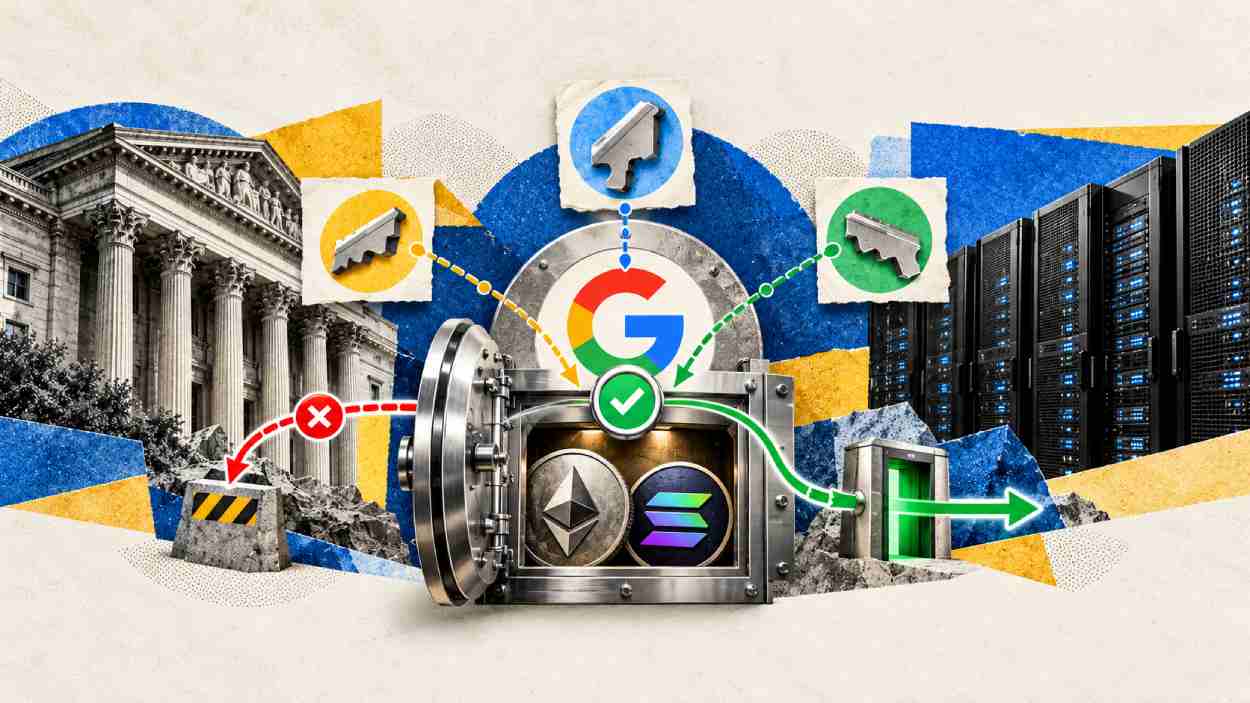
Google says the complete private key never sits in one place. A bank could hold one key share in Google Cloud, a second on its own hardware and a third with another cloud provider. When it moves assets, the transaction enters Google’s Confidential Space, a hardware-isolated computing environment. A policy engine there checks it against the bank’s rules before signing starts.
Those rules can cap transfer amounts, restrict destination wallets or require approval from several departments. Signing thresholds are adjustable too, such as two of three participants or five of seven. Google says customers keep control of their key material, which it cannot access unencrypted even when shares sit on Google infrastructure.
The service will support ECDSA and Ed25519 signing at launch. Google says post-quantum signing can follow as blockchains adopt it, but it gave no timetable.
Fireblocks, Fordefi and BitGo face a cloud-scale rival
Google argues that its banking relationships and security expertise give it an edge over specialist crypto custody providers. It is also courting banks that are wary of vendors competing for the same customers. Google pitches itself as a neutral supplier that lets institutions run their own custody businesses.
The share-splitting design is the core of that pitch. Banks get cloud convenience without handing any single provider, Google included, complete control of their signing credentials.
Key Theft Damages in Crypto Industry
Key theft has cost the industry billions of dollars over the years, a pattern that runs through the biggest crypto hacks. Chainalysis found that compromised private keys accounted for 43.8% of cryptocurrency stolen in 2024. In March, a hacker pulled about $25 million from stablecoin protocol Resolv through a compromised privileged-account key and flaws in its minting system.
June showed the wider damage. Attackers who compromised a Humanity Protocol foundation member’s private keys drained more than $32 million from at least 17 wallets. The project’s token then fell more than 80%.
The controls have limits. Pre-signing checks may block transfers that break preset rules, but a legitimate user tricked into approving a malicious transaction still poses a risk. Google’s protections address compromised credentials and unauthorized transactions, and a hypothetical break of the underlying cryptography sits outside their scope.
Even with shares spread out, banks may still depend on Google for parts of the software, transaction policies and operational infrastructure. For institutions in the preview, security rests on configuration, on how each signing participant is protected and on who can change approval rules.
Several details are still missing from Google’s disclosures:
- Which banks and design partners are testing the service?
- Which digital assets is Alphabet securing with it?
- What will the service cost?
- How do its signing speed and key recovery compare with existing custody products under independent testing?
The next fixed marker is commercial availability, which Google has scheduled for early 2027. Until then, the only named user of Google Multi-Party Compute is Alphabet itself.